

A Turning Point in Justice: Luigi Mangione Pleads Guilty to Stalking Charges in Federal Court
Luigi Mangione's Guilty Plea to Stalking Charges: A New Chapter in the Brian Thompson Case
The fast-food giant Chick-fil-A has recently disclosed a significant data breach, affecting thousands of customers who have used their Chick-fil-A One Loyalty program. The breach, which occurred from July 17 to July 19, 2026, allowed unauthorized parties to access customers' sensitive information, including names, email addresses, Chick-fil-A One membership numbers, and the last four digits of credit or debit card numbers. The compromised data also included customers' birthdays and addresses saved to their accounts, further exacerbating the security concerns.
According to Chick-fil-A, the data breach was detected after the company noticed suspicious login activity on certain Chick-fil-A One Loyalty accounts. An investigation was launched immediately, and the company subsequently took steps to address, secure, and restore the affected accounts. In a statement regarding the breach, a Chick-fil-A spokesperson emphasized the company's commitment to maintaining the trust of its guests, stating, 'We sincerely apologize for any inconvenience or concern this situation may have caused and remain committed to maintaining the trust our guests place in us every day.'
Following the breach, Chick-fil-A has taken several measures to mitigate the damage. The company has forced logouts on affected accounts, removed any saved payment methods, and restored affected Chick-fil-A One balances, as well as added additional rewards. Customers are also being advised to reset their Chick-fil-A passwords and keep a close eye on their credit reports and account statements for any further suspicious activity. This guidance aims to prevent any potential financial harm that could arise from the compromised data.
The incident serves as a stark reminder of the importance of robust cybersecurity measures in today's digital landscape. Companies must remain vigilant in protecting customers' sensitive information, as a single security lapse can have far-reaching consequences. It is essential for companies like Chick-fil-A to take proactive steps to prevent data breaches, invest in cybersecurity protocols, and educate customers on how to protect themselves in the aftermath of such incidents.
The data breach also highlights the need for more comprehensive regulations and guidelines in the data protection space. There is a growing concern that the current regulatory framework does not adequately address the complexities of modern data breaches. As a result, companies may be left to navigate the aftermath of such incidents without adequate support or clear guidance on responsible data handling and security practices.
Chick-fil-A's response to the data breach demonstrates the company's commitment to regaining the trust of its customers. While the incident is undoubtedly serious, it serves as an opportunity for Chick-fil-A to improve its cybersecurity measures and provide better protection for its customers. As the company moves forward, it will be essential to keep the affected customers informed and provide clear guidance on the steps being taken to prevent future breaches. In the long term, the incident may also prompt regulatory changes aimed at strengthening data protection and cybersecurity standards across the industry.
Chick-fil-A Data Breach: Thousands of Customers' Information Exposed WSFA
Luigi Mangione's Guilty Plea to Stalking Charges: A New Chapter in the Brian Thompson Case
A recent security incident involving a public Google Doc containing passwords has raised concerns...
A mysterious Wi-Fi network appeared on a Delta flight after a hacker convention, raising concerns...
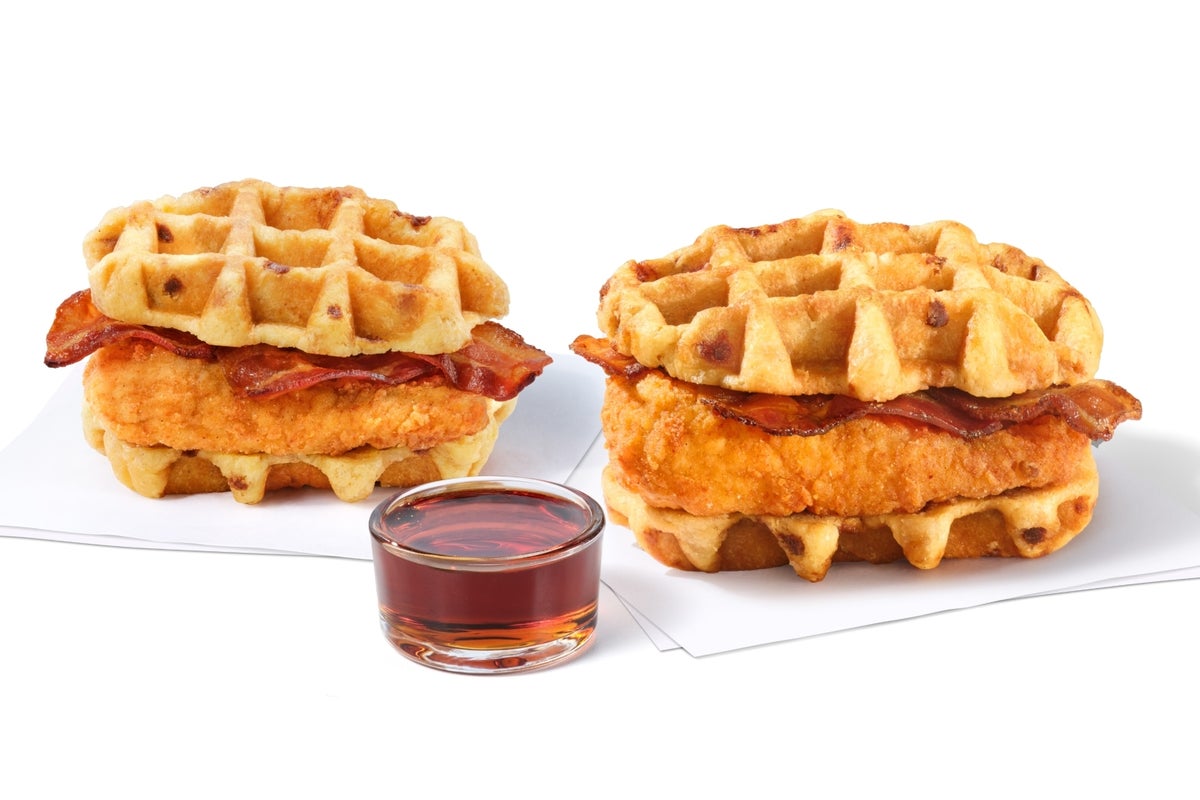
Chick-fil-A's Bold Move to Update Their Menu With the Delicious Chicken and Waffles Sandwiches and...
Chick-fil-A has unveiled its latest fall menu, featuring a range of innovative and unexpected...
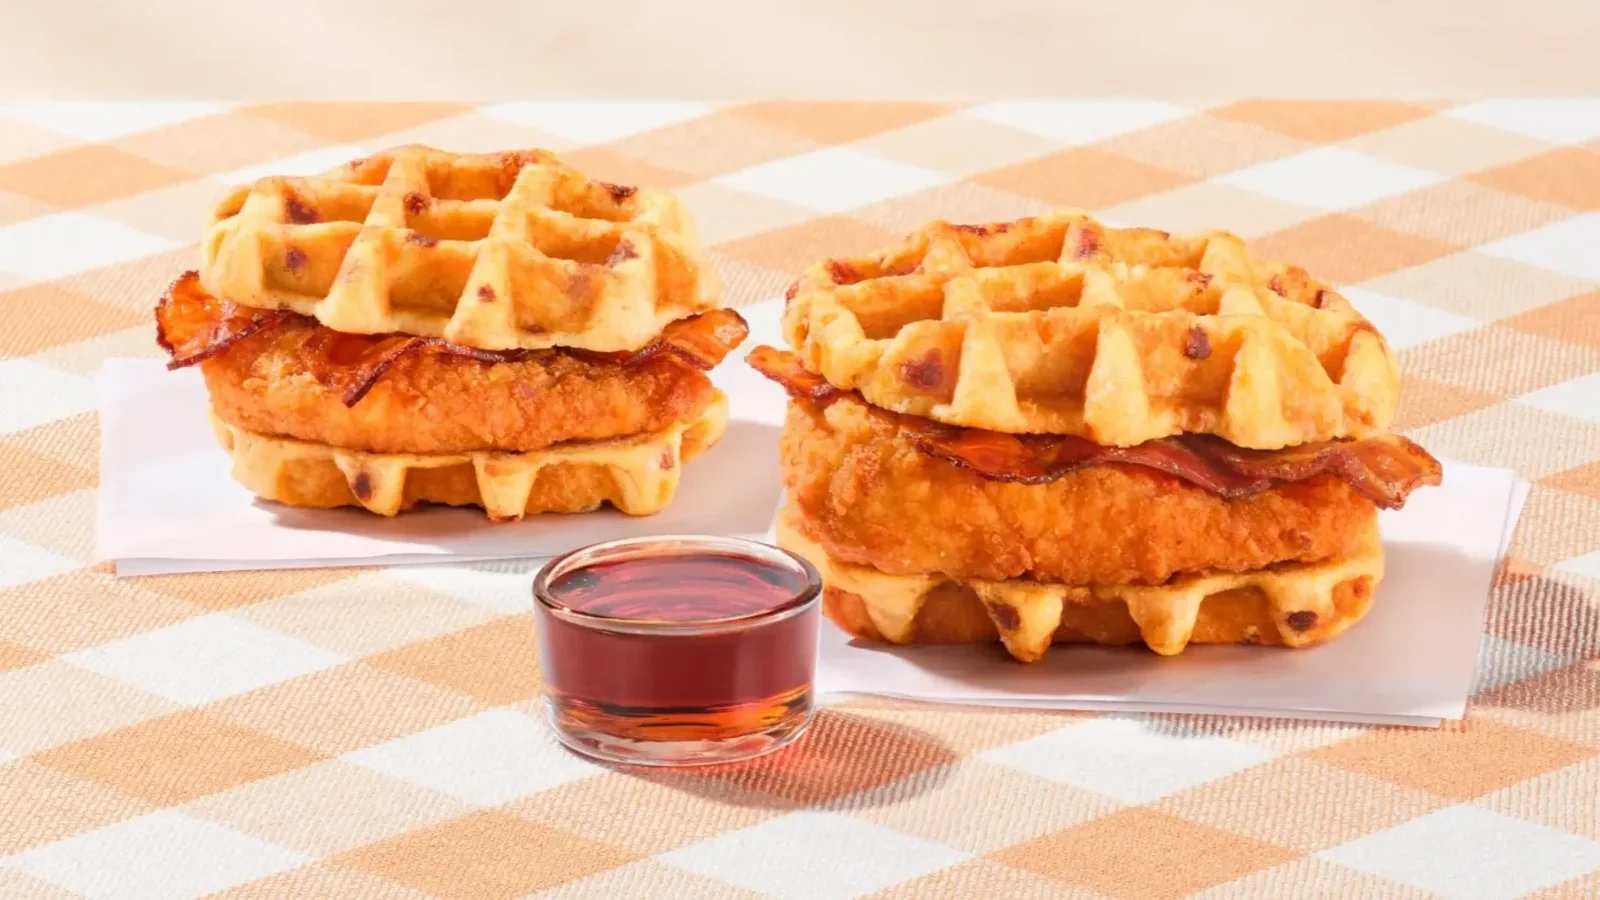
Get ready to indulge in a delicious twist on a classic comfort food favorite - Chick-fil-A is now...
Netizen tidak senang dengan komentar-komentar yang diberikan
BTS mungkin kembali mengikuti Grammy setelah rekanan mereka, Recording Academy, mengumumkan revisi...
BTS mungkin tidak akan mengubah keputusan untuk mengabaikan Grammy karena deadline pengiriman musik...
Update terbaru tentang keputusan BTS untuk tidak mengirimkan musik mereka untuk dijadikan nominee...
Pihak Recording Academy mengumumkan akan kembali meninju keputusan untuk memperkenalkan kategori...
Sangyeop Sangyeop mengumumkan rencananya untuk menikah dengan seorang non-celebrity, mengejutkan...