
Tragedy Unfolds: 5 People Shot Outside Virginia State University Dorms
A devastating shooting incident occurred outside Virginia State University dorms, leaving 5 people...

The Federal Bureau of Investigations has issued a warning about a phishing scam that targets Microsoft 365 users. This scam, known as Kali365, is a Phishing-as-a-Service platform that has been mainly distributed on Telegram.
Kali365 enables hackers to bypass multi-factor authentication without the need for a user's log-in credentials. Cyberattackers send phishing emails purporting to be a reputable cloud or document-sharing service, containing codes and instructions for visiting a real Microsoft verification page.
When the victim inputs the device code, they are unwittingly authorizing the cyberattacker's device to access their account. Once a cyberattacker has successfully pulled off the phishing scam, they have access to the victim's Microsoft services, including Outlook email, Teams, and OneDrive cloud service.
The FBI first detected the Kali365 phishing scam in April and has offered tips for protecting against the scam. It urges anyone who receives a suspicious email or notices suspicious logins from unauthorized devices to report them to the Internet Crime Complaint Center.
The FBI warns against opening links with access codes that have not been requested. Kali365 lowers the barrier of entry, providing less-technical attackers access to AI-generated phishing lures, automated campaign templates, real-time targeted individual/entity tracking dashboards, and OAuth token capture capabilities.
The FBI has issued a public service announcement to warn of a phishing scam targeting Microsoft 365 users, stemming from the Kali365 platform
A devastating shooting incident occurred outside Virginia State University dorms, leaving 5 people...
Exploring the historical context, key statistics, and expert insights surrounding the significant...
The FBI has announced a record decrease in violent crime rates for 2025, with a significant drop in...
A recent security incident involving a public Google Doc containing passwords has raised concerns...
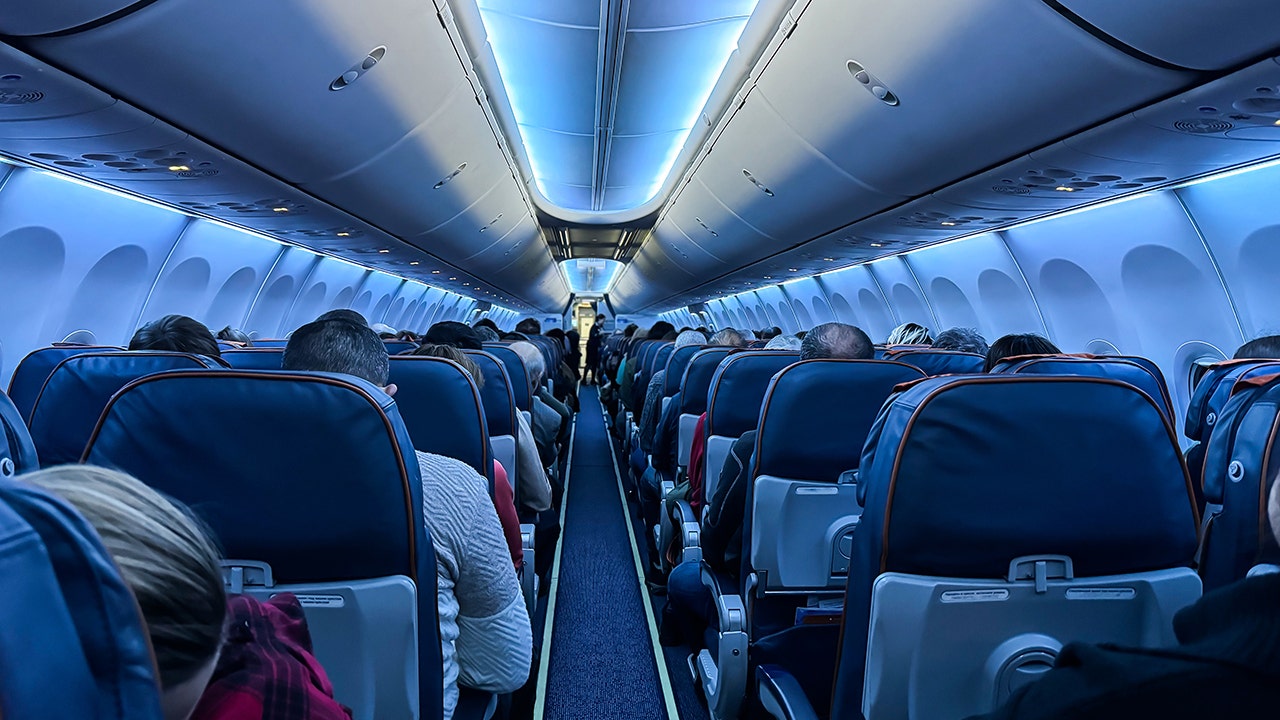
A mysterious Wi-Fi network appeared on a Delta flight after a hacker convention, raising concerns...
Brazil orders suspension of live streams on Discord following teenage girl's suicide
Netizen tidak senang dengan komentar-komentar yang diberikan
BTS mungkin kembali mengikuti Grammy setelah rekanan mereka, Recording Academy, mengumumkan revisi...
BTS mungkin tidak akan mengubah keputusan untuk mengabaikan Grammy karena deadline pengiriman musik...
Update terbaru tentang keputusan BTS untuk tidak mengirimkan musik mereka untuk dijadikan nominee...
Pihak Recording Academy mengumumkan akan kembali meninju keputusan untuk memperkenalkan kategori...
Sangyeop Sangyeop mengumumkan rencananya untuk menikah dengan seorang non-celebrity, mengejutkan...