Pemerintah Kabupaten Aceh Tamiang: Bumi Muda Sedia Pulih dan Bangkit
Pemerintah Kabupaten Aceh Tamiang: Bumi Muda Sedia Pulih dan Bangkit — Informasi Terbaru
Don't have an account? Sign up
Recently, we uncovered a vast malicious infrastructure distributing malware, malicious documents, remote desktop software, and phishing pages. The infrastructure was linked to a strange homepage that caught our attention.
EtherRAT is a RAT developed in Node.js that allows an attacker to gain complete control over the machine and execute arbitrary code returned by the Command and Control (C2) server. The malware uses the Ethereum blockchain to obtain the C2 server, making it more resilient to infrastructure takedowns.
While threat hunting, we found an open directory distributing MSI installers and PowerShell scripts, which ultimately distributed EtherRAT. In the analyzed cases, the PowerShell scripts and MSI installers were distributed from a '/install' folder. The versions have a progressive number, ranging from v1 to v10.
The returned home page caught our attention and prompted us to further explore the campaign.
Analyzing domains and associated IPs with the EtherRAT distribution, we detected other similar home pages with a hacking-style theme. These websites appeared to belong to a larger distribution chain, which also distributes phishing, remote control software, and other malware.
Interestingly, the majority of the domains related to this malicious infrastructure in the past also returned an HTML page related to a 'Bulletproof Infrastructure' service.
Stop threats before they can do any harm.
Malwarebytes Browser Guard blocks phishing pages and malicious sites automatically. Free, one click to install. Add it to your browser >
Gabriele is a Malware Research Engineer who loves fighting malware. When he's not doing that, you’ll find him enjoying nature, art, and animals.
Discover the scope of a sophisticated malware infrastructure distributing EtherRAT, phishing pages, and malicious software, uncovered by Malwarebytes
Pemerintah Kabupaten Aceh Tamiang: Bumi Muda Sedia Pulih dan Bangkit — Informasi Terbaru

Acara 600 ribu porsi kulinier gratis di Monas, menghidupkan semangat kebangsaan dan memperkuat rasa...
Hayden Panettiere, bintang televisi Amerika yang terkenal dengan perannya dalam serial 'Heroes' dan...
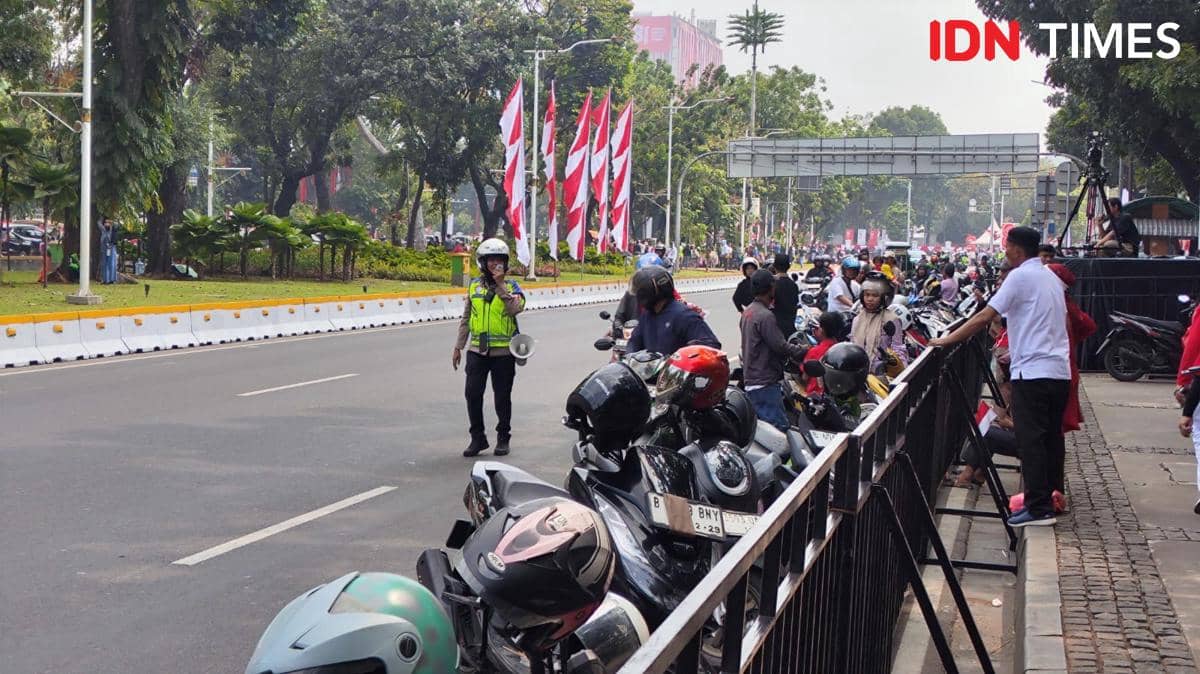
Jalan Merdeka Barat Dekat Istana Merdeka Jadi Parkir Liar Warga yang ke Monumen Nasional IDN Times

Kopassus Mengudara: Aksi Terjun Payung Terunggul di Istana Merdeka - Media Indonesia
Watch the live action of Tijuana vs. Cruz Azul, all the latest news, analysis, and match scores...
Netizen tidak senang dengan komentar-komentar yang diberikan
BTS mungkin kembali mengikuti Grammy setelah rekanan mereka, Recording Academy, mengumumkan revisi...
BTS mungkin tidak akan mengubah keputusan untuk mengabaikan Grammy karena deadline pengiriman musik...
Update terbaru tentang keputusan BTS untuk tidak mengirimkan musik mereka untuk dijadikan nominee...
Pihak Recording Academy mengumumkan akan kembali meninju keputusan untuk memperkenalkan kategori...
Sangyeop Sangyeop mengumumkan rencananya untuk menikah dengan seorang non-celebrity, mengejutkan...