
Security Breach: When Passwords Stored in Public Google Doc Show Up in Search Results
A recent security incident involving a public Google Doc containing passwords has raised concerns...
Chick-fil-A, one of America's leading quick-service restaurant chains, has confirmed a data breach involving unauthorized access to the company's customer loyalty accounts. This high-profile incident is believed to have originated from a combination of credential stuffing attacks, where hackers exploited reused usernames and passwords to access sensitive information. In a statement released to the public, Chick-fil-A emphasized the need for their customers to change passwords and implement two-factor authentication to protect their personal data.
Chick-fil-A Discloses Data Breach Following High-Profile Credential Stuffing Attacks
A recent security incident involving a public Google Doc containing passwords has raised concerns...
A mysterious Wi-Fi network appeared on a Delta flight after a hacker convention, raising concerns...
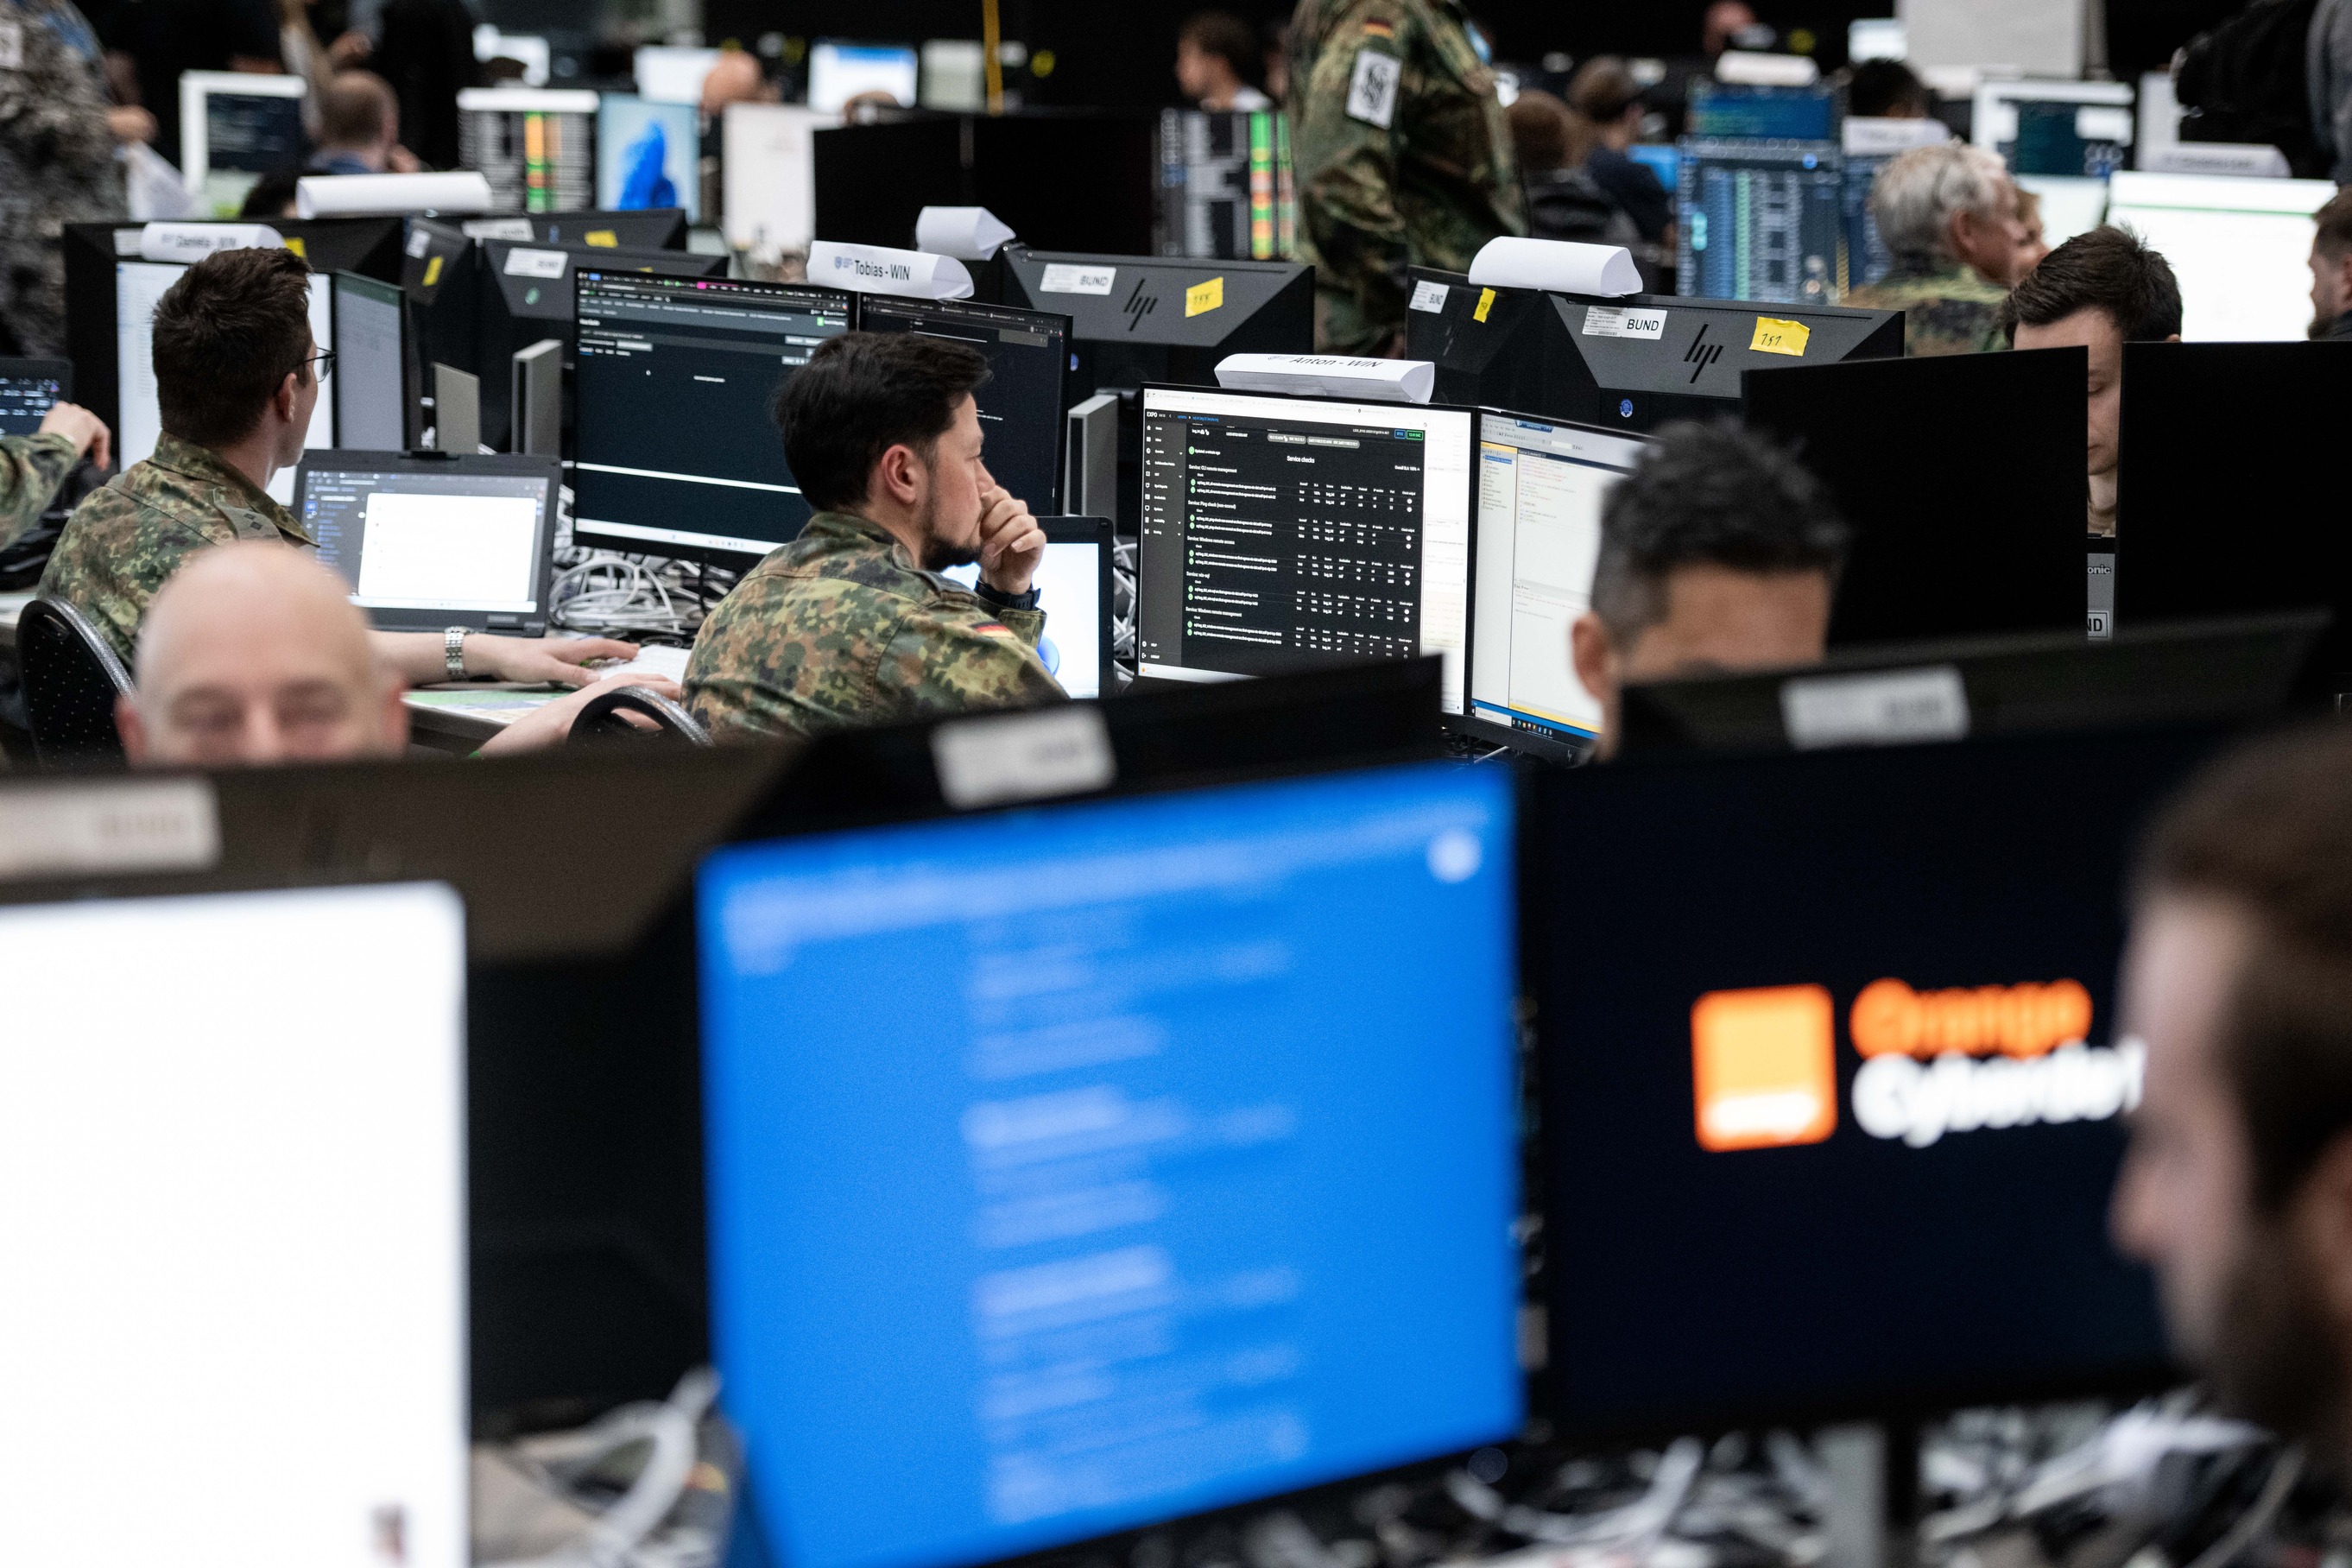
Boosting global cybersecurity, NATO and an AI startup have collaborated to assign and track...

Mashable investigates a proposed partnership between Flock Safety and Nexar to equip Uber and Lyft...
The Taiwanese government has decided to simulate a war scenario by intentionally slowing down the...

Get the inside scoop on Flock's secret plans for rideshare dashcam data, police coaching tactics,...
Netizen tidak senang dengan komentar-komentar yang diberikan
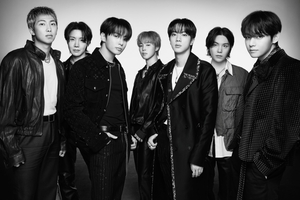
BTS mungkin kembali mengikuti Grammy setelah rekanan mereka, Recording Academy, mengumumkan revisi...
BTS mungkin tidak akan mengubah keputusan untuk mengabaikan Grammy karena deadline pengiriman musik...
Update terbaru tentang keputusan BTS untuk tidak mengirimkan musik mereka untuk dijadikan nominee...
Pihak Recording Academy mengumumkan akan kembali meninju keputusan untuk memperkenalkan kategori...
Sangyeop Sangyeop mengumumkan rencananya untuk menikah dengan seorang non-celebrity, mengejutkan...